SecurityX (Formerly CASP+) for Veterans: How to Tell If You're Ready
Michael got only rejections. Then a $100K facilities manager role.
Michael, E-7, Navy, tried a ton of outside help before BMR
CompTIA Advanced Security Practitioner (CASP+) is now CompTIA SecurityX, on the CAS-005 (V5) exam launched December 17, 2024. CompTIA's SecurityX page aims it "for security architects and senior security engineers" and recommends "a minimum of 10 years of general hands-on IT experience, including 5 years of hands-on security."
It's a recommendation, not a requirement to sit the exam. BMR's advice: the work you have led tells you more than your years do.
Score yourself on the four exam domains in the table below. Your score tells you whether to book now or wait.
Am I ready for SecurityX, or is it too early?
Run this check. The domains and weights are CompTIA's. The "ready when" lines are BMR advice. The duty examples show the kind of work, not a job code that qualifies you.
| Domain (share of exam) | You are ready when you have done this at work | A military duty that fits |
|---|---|---|
| Governance, risk, and compliance, or GRC (20%) | You wrote or owned security policy. You ran a risk assessment and can defend the rating. | An information system security manager (ISSM) keeping a system's risk decisions and compliance package current. |
| Security architecture (27%) | You designed network segments, secure zones or cloud controls. Keeping someone else's design running does not count. | A cyber planner who drew the boundary and zone layout for a new site or enclave. |
| Security engineering (31%) | You scripted fixes in PowerShell, Bash or Python. You ran scans and patching at scale. You set up encryption or certificate-based login. | An information system security officer (ISSO) who automated scan and patch reports for a whole enclave. |
| Security operations (22%) | You tuned alert rules, hunted threats and worked an incident to root cause. | A network defense lead who ran a cell from first alert to the after-action report. |
Count only the rows where you led the work. BMR's advice on the score: Three or four rows? Book the exam and study the gaps. Two or fewer? Get more seat time first.
Engineering is the biggest slice at 31%. CompTIA's objectives put scripting, automation and advanced cryptography there. If you have never scripted, start your study in that row.
CompTIA lists these exam facts on the same page:
| Exam fact | SecurityX (CAS-005) |
|---|---|
| Questions | Maximum of 90, multiple-choice and performance-based |
| Time | Maximum of 165 minutes |
| Passing score | Pass/fail only, no scaled score |
| Languages | English and Japanese, other languages to be determined |
Performance-based questions ask you to do the task itself. That's where your duty history helps most. To turn those duties into resume lines, see our military cyber careers guide. Still building the basics? Start with our Network+ guide for veterans.
What did the switch from CASP+ to SecurityX change for me?
If you hold CASP+, very little. CompTIA's rebrand post, dated December 18, 2024, says this:
"The name change to SecurityX will not affect the certification status of current CASP+ certification holders or the continuing education program. If you are an active CASP+ certification holder, you'll receive a notification to download the updated SecurityX badge."
So list the cert the way your record now shows it. BMR's advice: write "CompTIA SecurityX (formerly CASP+)" so both names match a job post.
If you studied for the old V4 exam, the weights moved. The same post gives the shift:
- Governance, risk, and compliance rose from 15% to 20%.
- Security architecture fell from 29% to 27%.
- Security engineering rose from 26% to 31%.
- Security operations fell from 30% to 22%.
Old V4 books underweight policy and engineering. Study from V5 material.
The exam page lists V5 retirement as "usually three years after launch (estimated 2027)." CompTIA calls that an estimate. Check the page before you book a late 2027 test.
Which DoD work roles accept SecurityX?
The Department of Defense (DoD) sets cyber job rules in DoD Manual 8140.03. CompTIA's DoDM 8140 page says: "By February 2025, all DoD civilian employees and military service members in DCWF work roles under the cybersecurity workforce element must be qualified in accordance with DoDM 8140.03."
The same page lists each work role and the CompTIA certs approved for it. In these five roles, the page lists no Security+ or Cybersecurity Analyst (CySA+) option. In the first three, SecurityX is the only CompTIA cert listed. CompTIA's page shows only CompTIA certs, so other vendors' certs may also count.
| Work role (code) | CompTIA certs the page lists |
|---|---|
| Research and Development Specialist (661) | SecurityX |
| Product Support Manager (803) | SecurityX |
| Information Systems Security Developer (631) | SecurityX |
| Enterprise Architect (651) | Cloud+, SecurityX |
| Security Architect (652) | Cloud+, SecurityX |
Now the other side. For roles 511, 531, 541 and 461, the page also lists Security+ and CySA+. You do not need SecurityX for those. The page lists Security+ and SecurityX for Information Systems Security Manager (722) too.
One catch. This list comes from CompTIA. DoD keeps its own matrix behind a login. Read the job announcement for its work role and cert rule before you pay. The wider rules are in our DoD 8140 guide. For the federal series many cyber jobs sit in, see our OPM 2210 guide.
SecurityX or CISSP first?
The Certified Information Systems Security Professional (CISSP) comes from ISC2. ISC2's experience rules say: "Candidates must have a minimum of five years cumulative, full-time experience in two or more of the eight domains of the current CISSP Exam Outline."
CompTIA's 10 and 5 years are a recommendation. ISC2's five years are a condition of holding the CISSP.
SecurityX can help with that condition. ISC2 says "an additional credential from the ISC2 approved list may satisfy up to one year." Its list names "CompTIA SecurityX" and "CompTIA Advanced Security Practitioner (CASP+)," and also "CompTIA Security+" and "CompTIA CySA+." If you already hold Security+, you already have that year.
Short on years? ISC2 offers a second route. "A candidate who doesn't have the required experience to become a CISSP may become an Associate of ISC2 by successfully passing the CISSP examination." The Associate then has six years to earn the five.
BMR's advice: under five years of security work? Check what you already hold. ISC2 lets one listed cert cover up to one year. So does a bachelor's or master's in computer science, IT or a related field. Have neither? SecurityX first can shave a year off the CISSP wait. Have one already? SecurityX adds no more.
Past five years in two domains, pick the one your target postings name. For the rest of the field, see our cybersecurity certifications guide.
What do the jobs it points to pay?
These are Bureau of Labor Statistics (BLS) figures for two jobs near this cert. They describe the jobs, not SecurityX holders.
| Job (BLS) | Median pay, May 2025 | Related work experience |
|---|---|---|
| Information security analysts | $129,180 | Less than 5 years |
| Computer network architects | $134,050 | 5 years or more |
BLS lists a bachelor's degree as typical entry education for both. Look at the experience column. The architect job expects the kind of years SecurityX is built around.
Who covers the SecurityX exam?
GI Bill: VA test fee refunds
The Department of Veterans Affairs (VA) refunds approved test fees, per its licensing and certification tests page. The cap is "no more than $2,000 per test," for a job that requires a license or certification. Each refund is charged to your entitlement.
VA says "Your benefits will cover only tests approved for the GI Bill." We did not check whether SecurityX is on that list. Check VA's test tool for SecurityX first. VA adds: "If you don’t see a test listed, it may be a valid test that's just not yet approved." You file the claim on VA Form 22-0803.
Still in the Army: COOL funding
Soldiers still in uniform can use Army Credentialing Opportunities On-Line (COOL). COOL helps soldiers find certifications, and its Credentialing Assistance (CA) program helps pay for them. The Army benefits page sets these limits:
- "Annual cap decreased from $4,000 to $2,000."
- "Limit Soldiers to one credential a year and a maximum of three in 10 years."
- Effective March 19, 2026, "Commissioned Officers (O1-10) are ineligible for CA."
A commissioned officer may still request funding to complete a credential goal. That goal must have been submitted before March 19, 2026 and not finished yet. The rule names commissioned officers, O-1 to O-10. The page does not mention warrant officers. Warrant officers should ask their education center how it applies.
SecurityX is not named on that page. Look it up in COOL before you ask for funds. This page checked only the Army's rules. For CompTIA's own pricing, see our CompTIA military discount guide.
Exam details checked November 2026 on CompTIA's SecurityX pages. Work roles came from CompTIA's DoDM 8140 page, and CISSP rules from ISC2. Funding came from VA and Army COOL, and pay from BLS.
What to Do Next
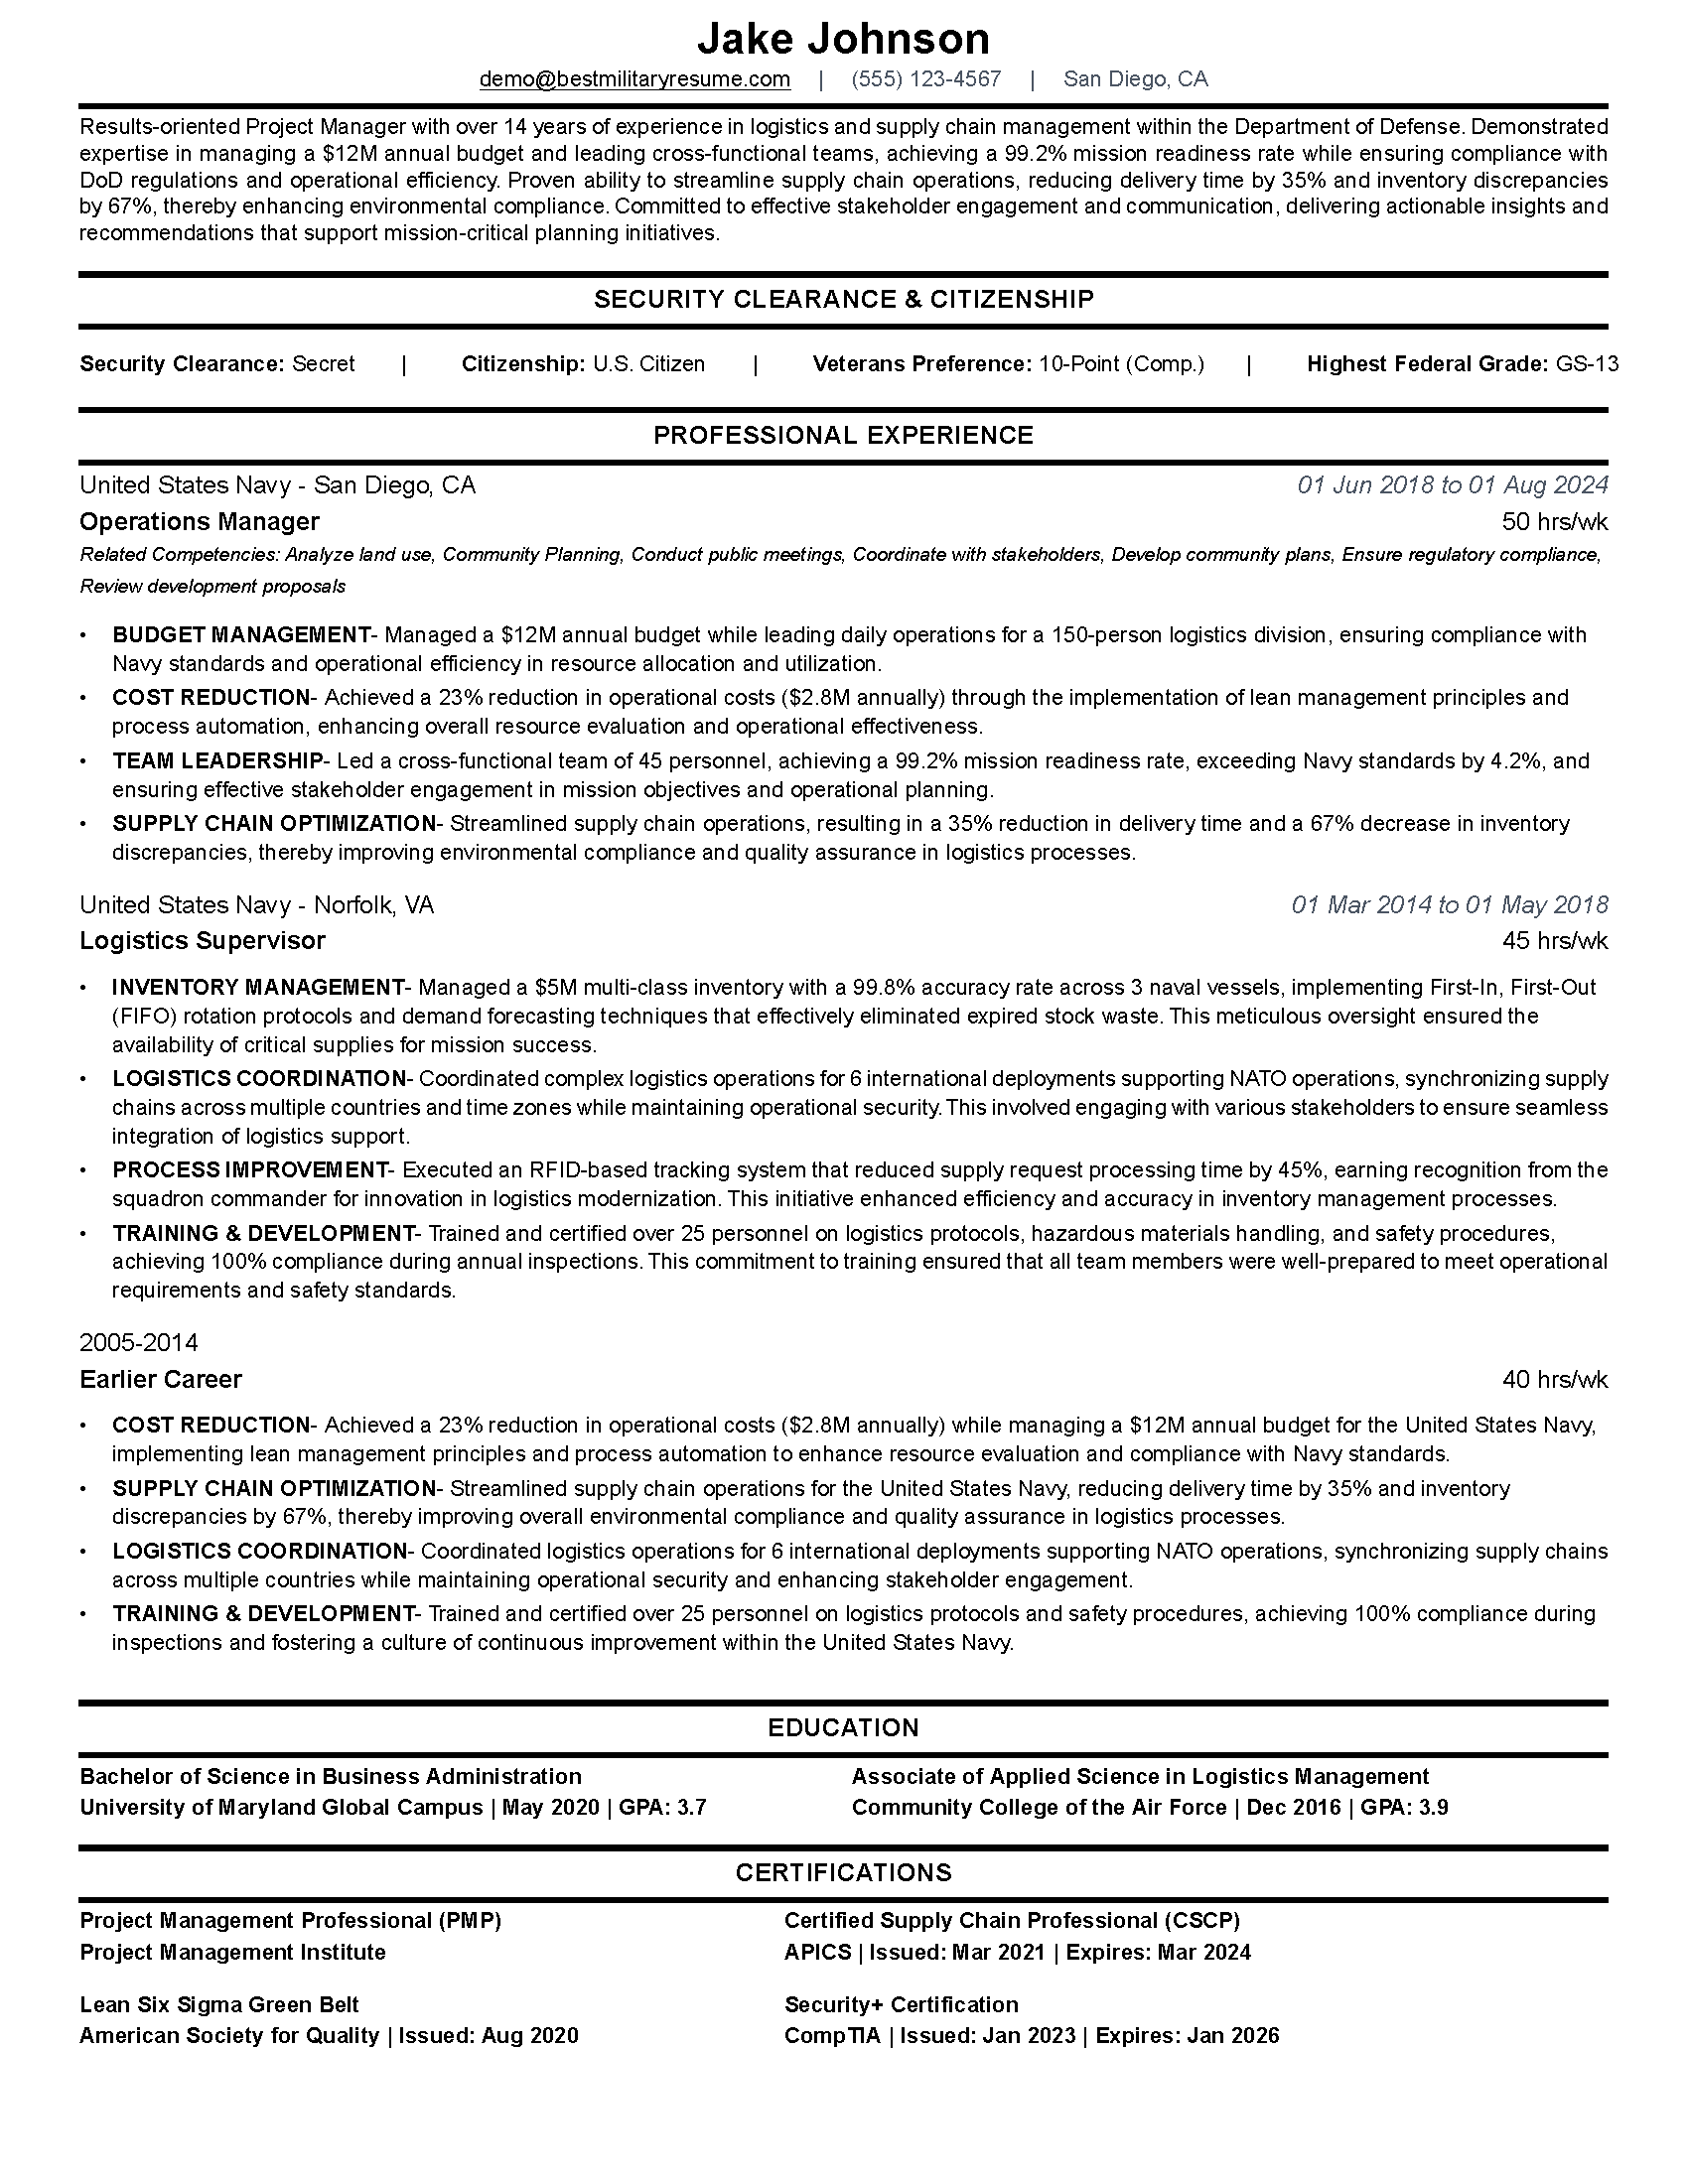
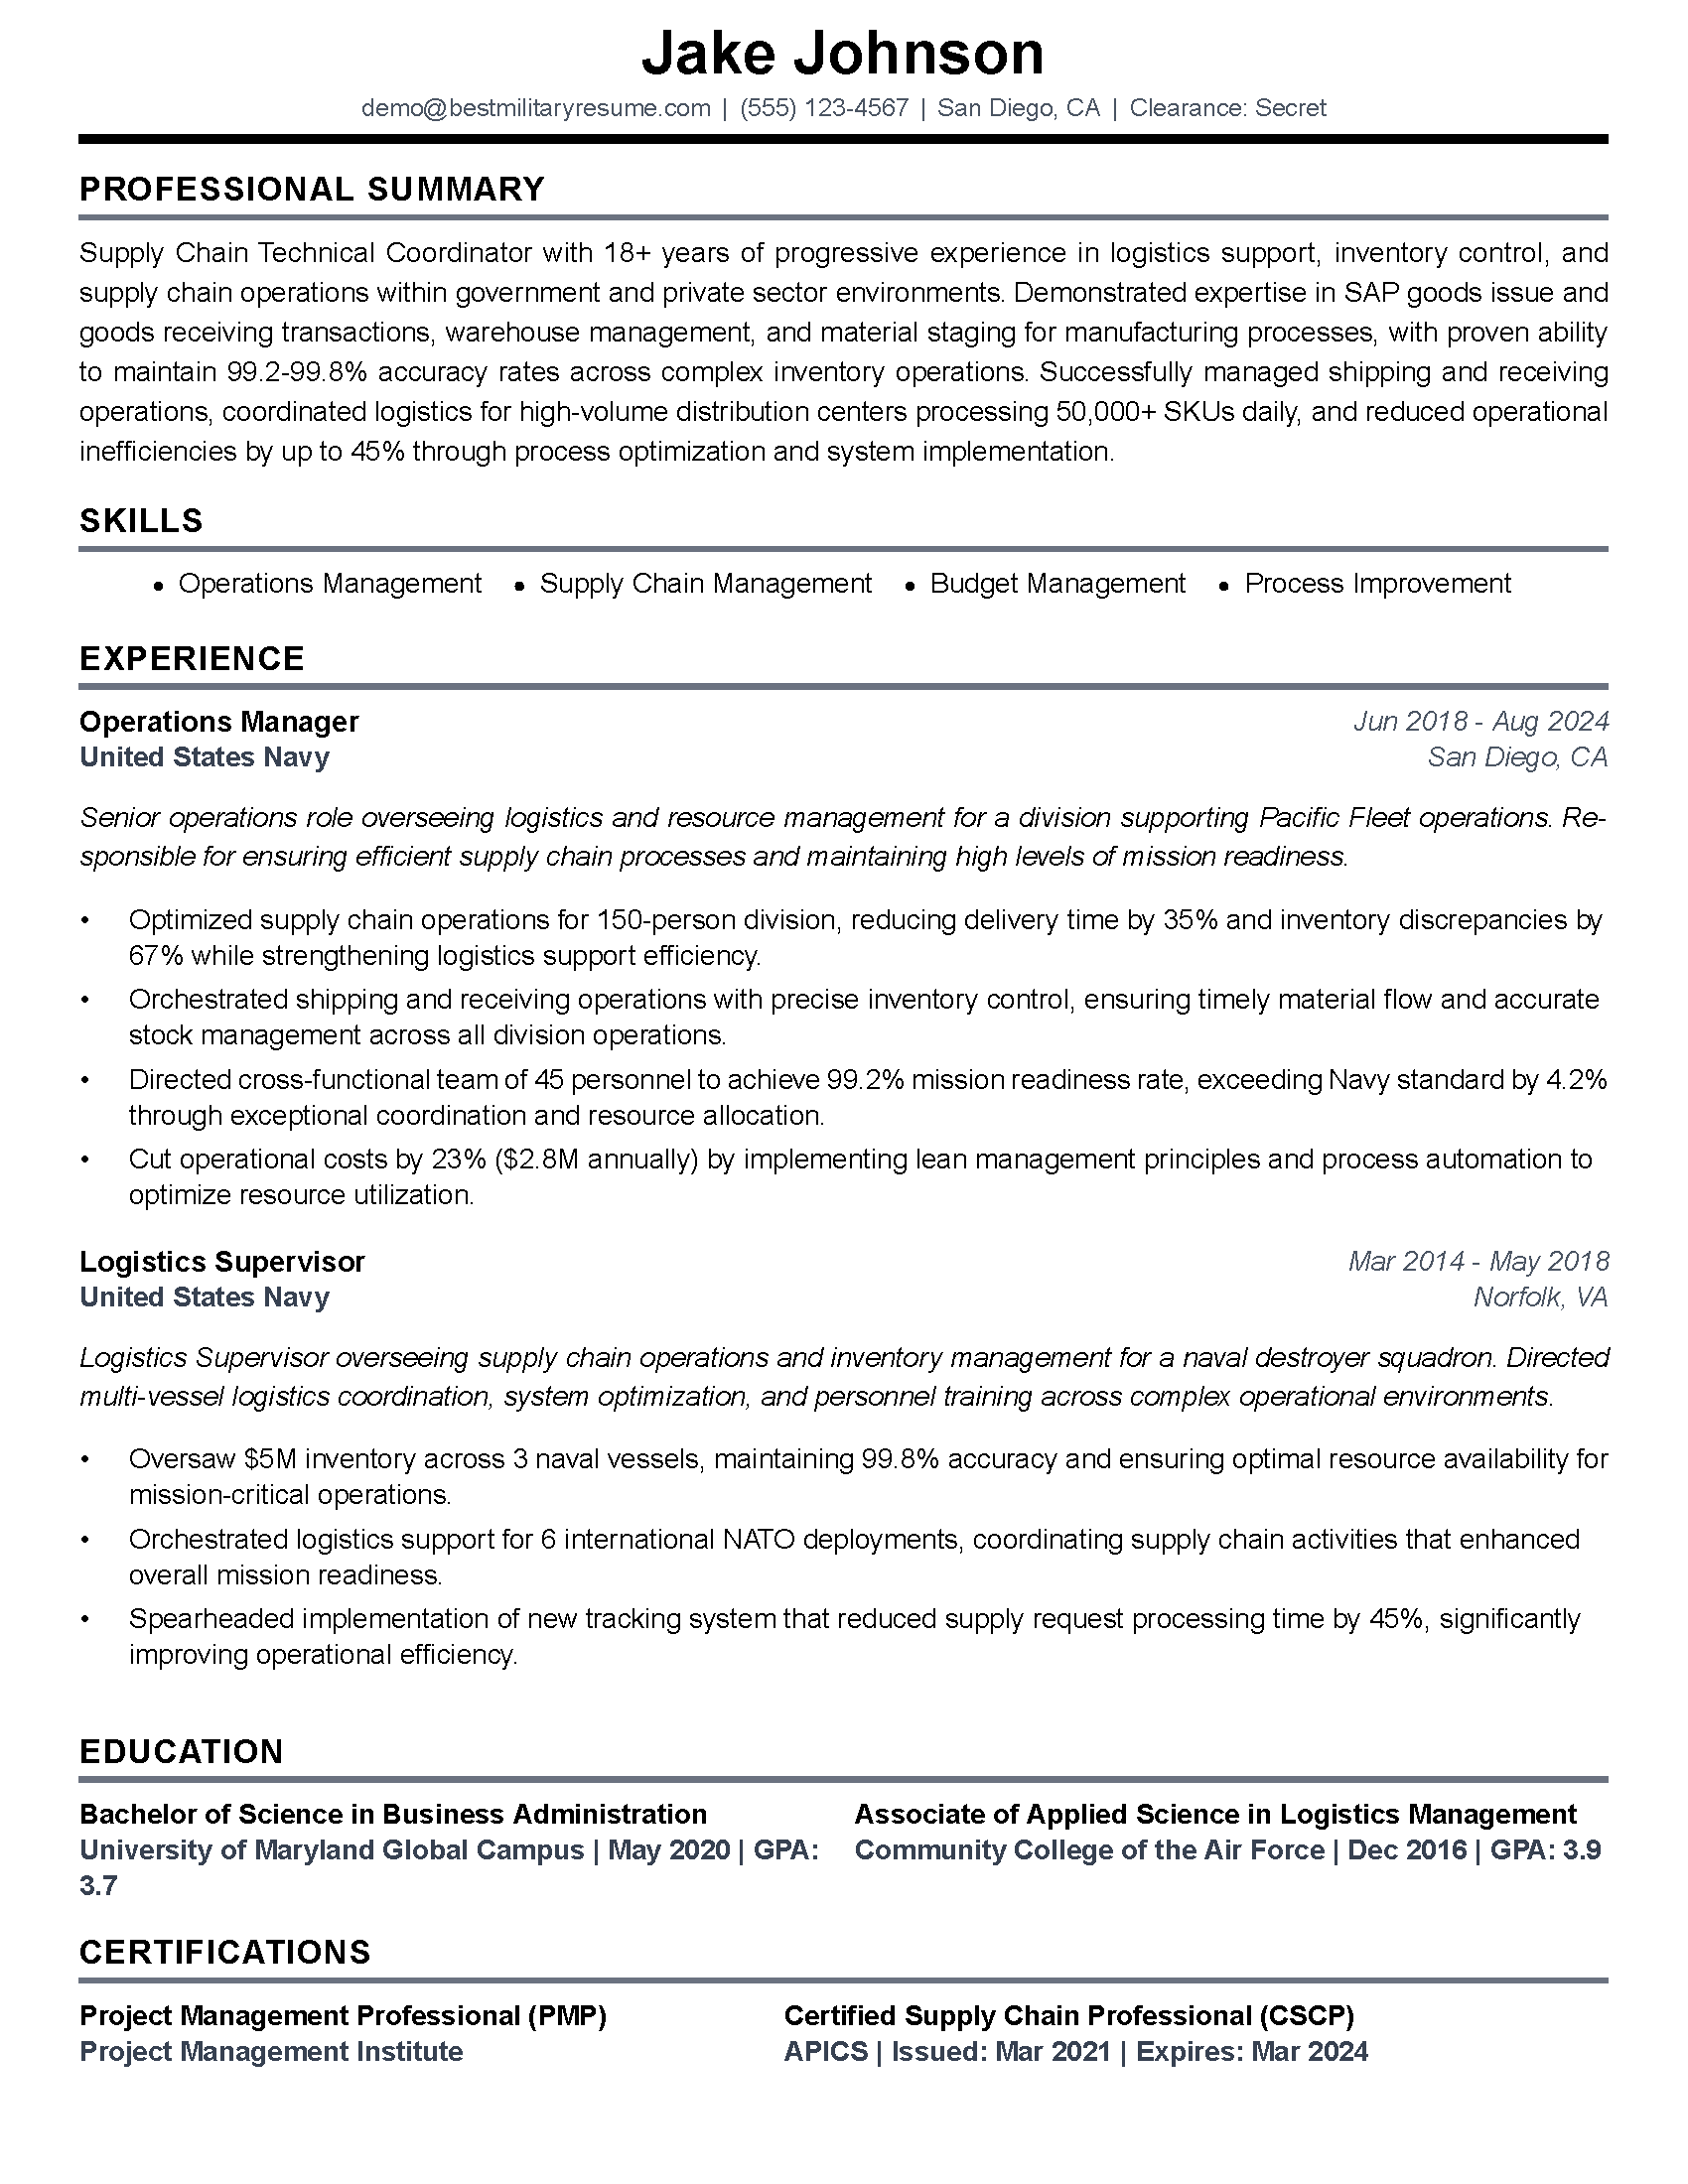
Your best self-check rows are your strongest resume lines. Put them up front, and aim them at a senior security engineer or architect posting you want. The military resume builder reads that posting and tailors your bullets to it. Cristian gave the Coast Guard 20 years, finishing as a Chief Warrant Officer 2 (W-2). He wrote in after his search:
"Landed a job as a Senior Security Analyst using BMR, add that to the count!"
Frequently Asked Questions
Do I need Security+ before I can take SecurityX?
How many exam objectives did SecurityX drop from CASP+ V4?
Is SecurityX an accredited certification?
Does the GI Bill pay for a SecurityX prep course?
About the author
Brad Tachi is the CEO and founder of Best Military Resume and a 2025 Military Friendly Vetrepreneur of the Year award recipient for overseas excellence. A former U.S. Navy Diver with over 20 years of combined military, private sector, and federal government experience, Brad brings unparalleled expertise to help veterans and military service members successfully transition to rewarding civilian careers. Having personally navigated the military-to-civilian transition, Brad deeply understands the challenges veterans face and specializes in translating military experience into compelling resumes that capture the attention of civilian employers. Through Best Military Resume, Brad has helped thousands of service members land their dream jobs by providing expert resume writing, career coaching, and job search strategies tailored specifically for the veteran community.